AI Governance

Responsible AI. Not banned, enabled.

Responsible, traceable AI, aligned with European standards for data protection and trustworthy AI. Built into the architecture from the start.

Stance

Governance is a leadership task.

AI governance is first and foremost a leadership question. And leadership doesn't respond with bans, a ban is the admission that you've stopped steering. Leadership sets the direction: clear guardrails, enablement and training, plus vetted solutions people are actually allowed to use.

Where leadership stays silent, a vacuum forms. Then every department finds its own way, every team picks its own tool: and business-critical data flows, uncontrolled, into third-party services. Böser Wille steckt selten dahinter, meist hat schlicht niemand den besseren Weg angeboten. Once it has leaked, no one gets it back.

Good governance fills that vacuum with better offers instead of bans. It states clearly what's allowed, makes the safe path the easy path, and gives people the means and the knowledge to use AI well.

What we mean by it

What effective AI governance is made of.

Governance isn't a document in a drawer, it's the interplay of five building blocks. Only together do they create control instead of standstill, and a tailwind instead of friction.

  1. Guardrails, not bansClear, simple rules about what is allowed, what isn't and why. That gives everyone boundaries they can work with, instead of grey zones each person reads differently.
  2. Enablement and trainingPeople learn to use AI safely and sensibly. Once someone understands what a model can do and where its limits lie, they can use it responsibly without a ban.
  3. Approved paths and toolsVetted models and concrete solutions on offer, so nobody has to fall back on a private browser tab. The safe path should also be the convenient one.
  4. Clear accountabilityRoles and bodies that decide and stand behind their decisions. Governance needs someone who owns it, otherwise it stays on paper.
  5. TraceabilityWho did what, when, and on what basis? It is fully logged and can be audited at any time, and that is where trust comes from.

Why governance

Guide

How to build AI governance: structures, roles and the path to control

The five building blocks from inventory to auditability, the roles it takes, and what ISO/IEC 42001 delivers, and what it does not.

Read the guide →

Bans only breed shadow IT.

Your people already use AI, the only question is whether it's under control or in a private browser tab. A blanket ban just moves the risk to where no one is looking.

And that is where it gets dangerous: without clear rules, confidential information, contracts, design data, customer data, ends up in third-party AI services, uncontrolled, somewhere in the world. Once it has leaked, no one gets it back.

Good governance doesn't put on the brakes, it enables. It gives clear answers instead of uncertainty: sensible rules and limits, and, above all, vetted AI and vetted, preferably local language models front and center. So your teams can work with a tailwind instead of in the shadows.

No model without a review. Developers don't wire just any LLM into new or existing tools because it happens to be convenient. Every model that goes into products and processes passes an honest assessment first:

Cybersecurity

How secure is the model itself: data leakage, attack surface, supply chain?

Hallucinations

Where does the model make things up, and how do we catch that in operation?

Bias

What distortions does it bring, and are they tolerable for the use case?

Backdoors & provenance

Where does the model come from, what's inside it, whom do we trust and why?

Only once a model passes these questions does it earn trust, and a place in your landscape. Where it comes to the security of the models themselves, this meshes closely with our Cybersecurity.

The real bottleneck

The bottleneck isn't the policy. It's operationalization.

Most organizations already have guidelines, the first governance structures, perhaps a policy document. The sticking point isn't the paper. It's the step into reality: which AI is actually in use, on what data, with what permissions? That's where control is decided.

Usually in place

  • AI guidelines and policies
  • first governance structures
  • security and compliance requirements

Usually missing

  • transparency over the AI systems actually in use
  • technical control and approval capability
  • assessment models, architecture governance, lifecycle steering
  • monitoring of data flows, APIs and agentic systems

Many organizations still cannot answer these questions today.

Which AI systems are actually in use?

What data is processed, which models are used?

Which APIs and tools have access?

How are agentic-AI systems controlled?

How are risks assessed and approved?

How is it monitored and traced in operation?

Our approach

Governance that comes from the architecture.

Deterministic, not autonomous

AI interprets results but doesn't plan its own chains of calls. People decide.

Identity & least privilege

Access via existing identities and permissions, no one goes beyond their own rights.

Fully auditable

Who, when, what, on what basis, completely traceable, centrally logged.

European-sovereign

AI on European infrastructure. Your data stays in Europe.

Services

From assessment to operating model.

Solid methodology rather than a tool or a license model: we assess real AI landscapes, define controls and anchor steering where it works: in architecture, operations and the organization. Governance, enterprise architecture and managing complex landscapes have always been our craft, and AI governance follows naturally from them.

Entry

Find your bearings

Quick clarity on maturity, usage and risks, a solid starting point.

  • AI Governance Readiness AssessmentMaturity of structures, usage, risks and roles.
  • AI Risk & Use-Case ClassificationCategorise systems by criticality, data sensitivity and requirements.
  • AI Supplier & Model AssessmentEvaluate external providers, models, hosting and security.
  • AI Tool Approval FrameworkStructured approval processes and governance gates.
Core

Operationalise technically

Where governance, architecture and security converge. Our differentiator.

  • AI Governance & Security AssessmentAn integrated view of governance, security, architecture and operational readiness.
  • AI Architecture & Controls ReviewReview system landscapes, data flows, APIs, RAG and agentic structures.
  • AI Lifecycle GovernanceApproval, change and monitoring processes with clear gates.
  • AI Governance Operating ModelRoles, bodies, decision and steering logic.
  • AI Control CatalogueReusable governance, security and architecture controls.
Strategic

Steer the enterprise

Governance as part of the operating model, platform and lifecycle, at group level.

  • Enterprise AI Operating ModelIntegrated governance, platform steering, bodies and lifecycle.
  • AI Architecture GovernanceSteering for system landscapes, agentic AI and hybrid platforms.
  • AI Lifecycle & Transformation GovernanceRollouts, model changes and change management.
  • AI Governance Capability ModelMaturity and capability models for lasting AI capability.

In the works: governance automation (controls, monitoring, evidence collection), AI red teaming and advanced AI security, and managed services.

Orientation

Aligned with the relevant frameworks.

We design AI governance along the relevant European frameworks, by design from the outset.

ISO/IEC 42001 is the backbone here: the international standard for AI management systems. It mainly describes the organizational layer: management system, roles, processes, documentation, risk management. Technical operationalization: architecture, data flows, APIs, agentic AI, security, begins where the standard ends. That's exactly the bridge we build.

EU AI Act EU Data Act GDPR

Certified to ISO 9001. Our alignment with ISO/IEC 42001 is not a paper exercise: we run an AI management system of our own, covering our productive AI process, AI-assisted document processing at our Gelsenkirchen site. Deliberately narrow in scope, properly documented, with clear exclusions, exactly what we recommend to our clients: start with one process that genuinely holds up, then take on the next. Formal certification is in preparation. The same stance applies to everything else we do: responsible, traceable AI, aligned with European standards, with governance built in by design.
An attestation confirms a management system that is already in practice, so the work to that standard begins well before the certificate. Security and governance have been part of our baseline from the start.

The remaining framework references (EU AI Act, EU Data Act) position the solution design and are not presented as proof already achieved.
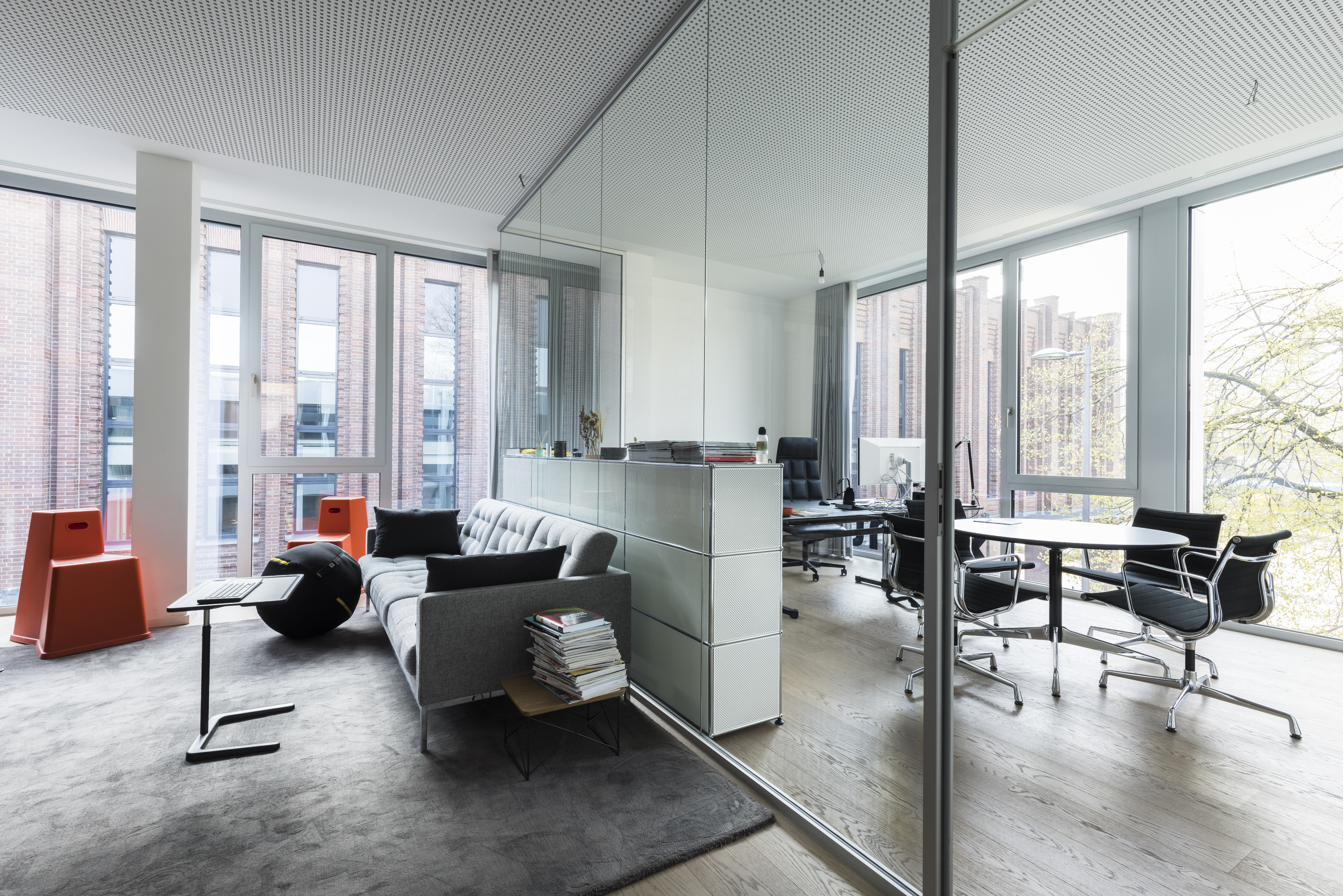
Modern Xient office with a lounge and meeting area

End-to-end

From strategy to audit.

Governance target state and guardrails, architecture and implementation, identity and access concepts, gapless auditability in operation, all from one source.

Clarity in governance, too. Not just in the data.

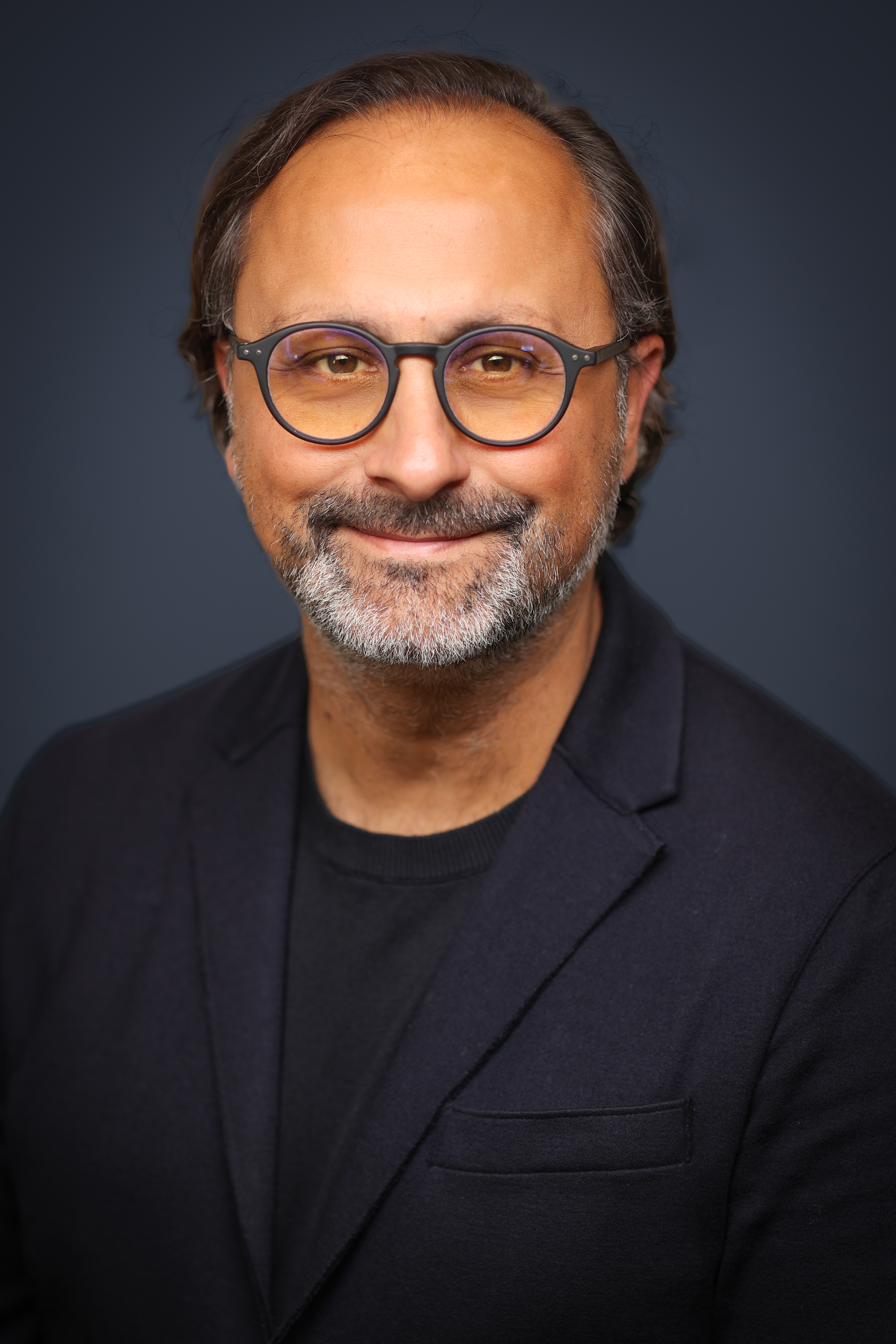
Yavuz Yıldız, Founder and Managing Director of Xient

Who's behind it

Governance that someone owns.

Our AI governance is owned by Yavuz Yıldız, Founder and Managing Director of Xient. For him, responsible AI is an executive matter. He sees it as a clear framework that makes AI accountable and secure, carried by architecture, processes and evidence that hold up in operation.

Yavuz Yıldız · Founder & Managing Director

In practice

Three products make governance tangible.

The three fit together, depending on where you stand. Answer the question that matches you.

"Which language models can we even trust?"

Xient Trusted LLM Private Beta

A continuously maintained catalog of vetted language models with a Trust Score. You pick the right model, and apply your own security policies on top.

Ideal when you want to adopt AI but first need clarity on which models you can trust.

Xient Trusted LLM →

"How do we keep our data entirely in-house?"

Xient Local LLM Pilot phase

The chosen model runs locally on your own hardware: advised by us, tuned to your purpose and securely operated. As much local as possible, as little cloud as necessary.

Ideal when data sovereignty comes first and as little as possible should leave your own environment.

Xient Local LLM →

"How do we use our SAP knowledge safely via AI?"

Xient Bridge Pilot phase

Governed AI on your vetted SAP data, in natural language inside Microsoft Teams, read-only first, curated and fully auditable.

Ideal when you want to make existing SAP knowledge accessible without giving up control.

Xient Bridge, governance-first AI in daily work →

Where governance meets confidentiality and protection, the path continues to Cybersecurity.

Bring AI securely in-house.

We'll show you how governance, security and impact work together, on your topics.

Book a confidential slot with Yavuz Yıldız directly, for a conversation about AI governance.

Or write to us: via the contact form · +49 221 16533980